
Start With the Information the Team Will Actually See
“Back-office support” is too broad a unit for a security review. A certificate of insurance request may expose names, policy numbers, and coverage details. A commercial renewal can add financial and loss information. Employee benefits work may involve information with additional handling requirements. The agency should name each workflow, the systems it touches, and the data needed to complete it before asking for a generic provider security questionnaire.
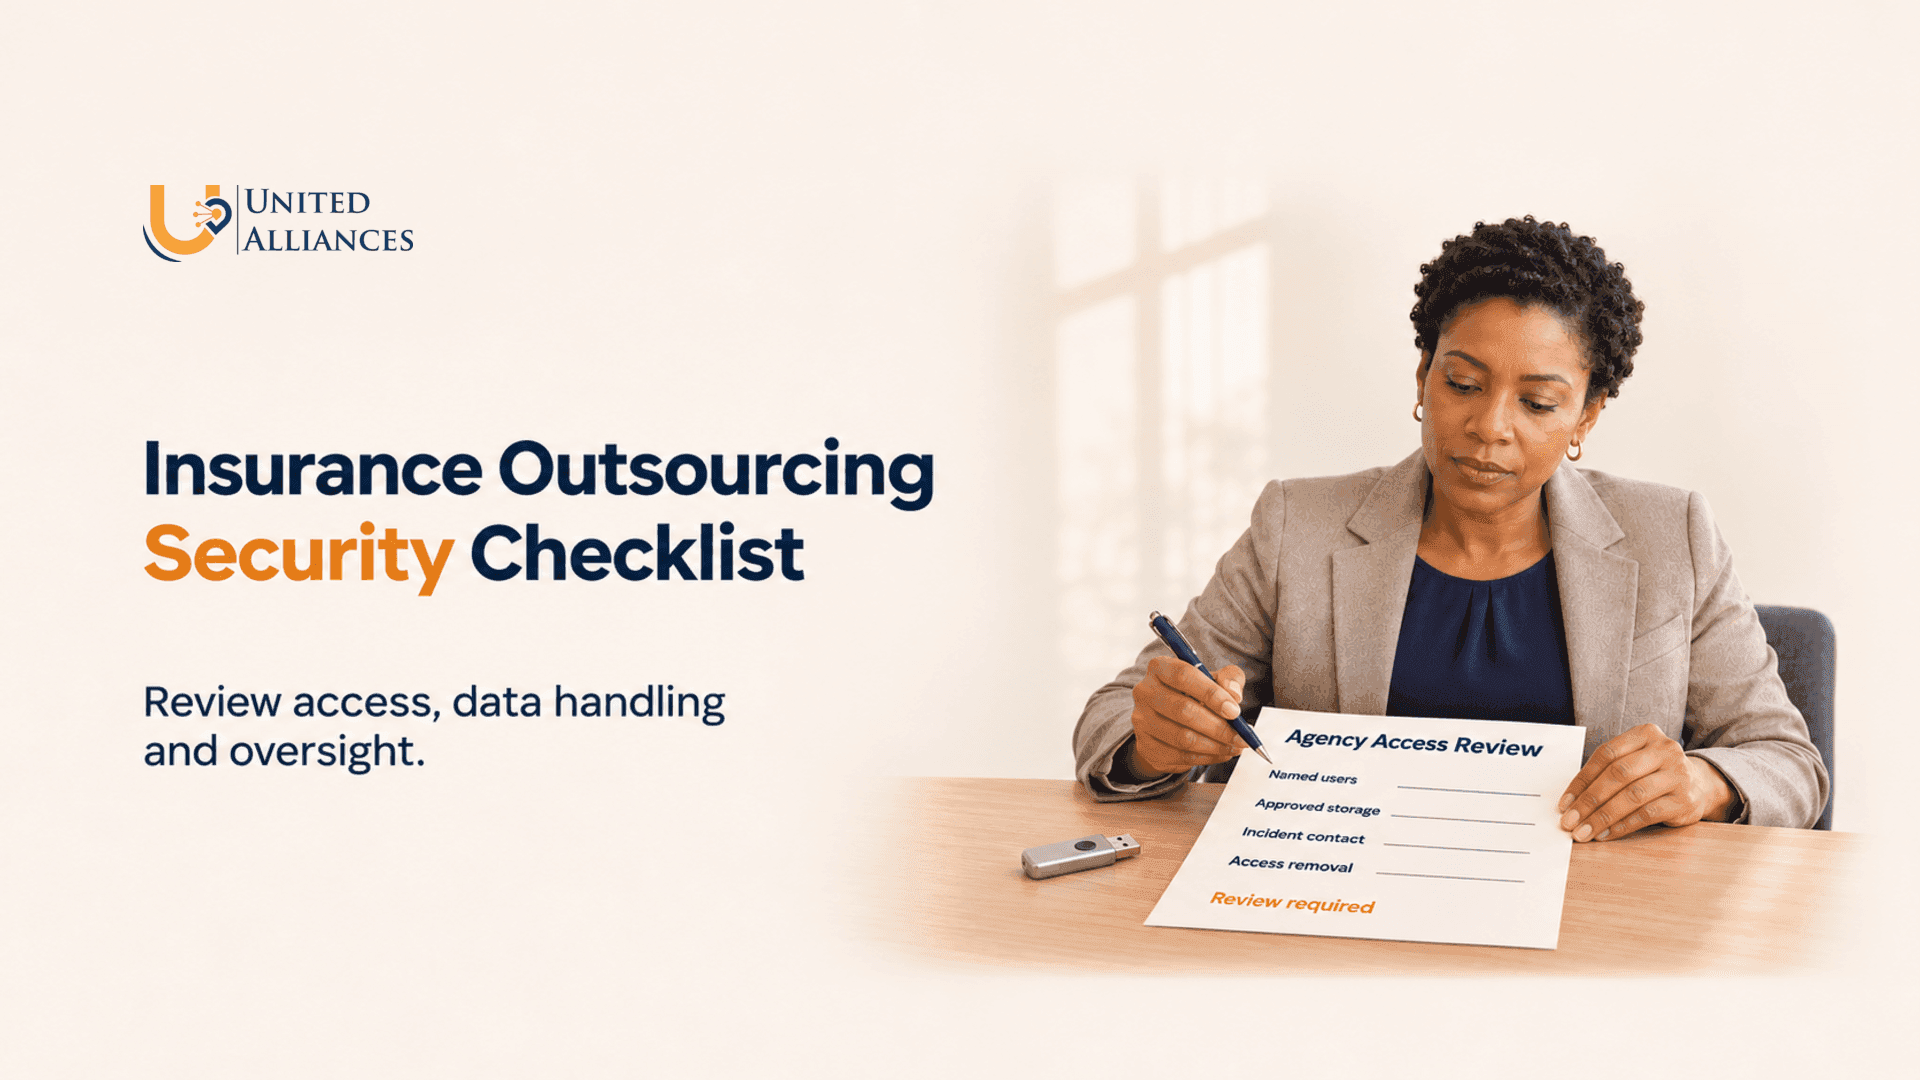
For each proposed task, record four facts: the source of the request, the records the assistant may view or edit, the person who approves the output, and the location of the final record. If the team only needs to prepare a draft, do not grant it permissions intended for issuing, binding, deleting, or bulk exporting. The review should also cover carrier portals and shared mailboxes, not just the agency management system (AMS).
The NAIC Insurance Data Security Model Law includes due diligence and appropriate safeguards for third-party service providers in its model provisions. It is a model, not a single nationwide rule. States adopt and implement requirements differently. For example, Pennsylvania's insurance department describes its own third-party oversight requirements under Act 2 of 2023. The agency should check its applicable state rules, carrier agreements, client commitments, and the data involved with its compliance lead or counsel.
Insurance Outsourcing Security Checklist: What Evidence Should You Request?
Use the same task packet with every candidate. “We have a policy” is a starting answer; the decision is whether that policy applies to the people, systems, and data in your proposed engagement. Ask for redacted examples or a walkthrough where sharing a full document would expose sensitive controls.
| Review point | Evidence to request | Decision before live access |
|---|---|---|
| Scope and confidentiality | Written task list, permitted uses of client data, confidentiality terms for staff and any third parties | Identify what the team may do and who can see the records |
| Named system access | Sample access request, role matrix, MFA method, approval and removal procedure | Assign each user only the permissions needed for the task |
| Devices and file transfer | Remote-work rules, approved transfer and storage locations, download and printing restrictions | Decide where a working copy may exist and how it is removed |
| Subcontractors and tools | List of people or entities that may touch the work, approved software, process for changes | Require review before an unapproved person or tool receives data |
| Record integrity | Sample AMS activity, document naming rule, exception log and reviewer handoff | Keep a traceable source, action, owner and approval for each file |
| Monitoring and incidents | Example access review, escalation contacts, response procedure and notification terms | Agree who receives an alert and what facts are supplied first |
| Continuity | Backup staffing procedure and permission process for a substitute | Ensure absence coverage does not silently expand access |
| Exit | Access revocation steps, return or deletion process and confirmation method | Account for open work, copies, credentials and retained records |
This is a buyer's review tool, not a declaration that any provider meets a legal standard. NIST's Cybersecurity Framework supply-chain guide supports defining supplier responsibilities and security requirements before a relationship begins and managing them during it. Make the agency's approval owner and evidence location part of the checklist, so someone can reopen a decision when the scope changes.
What Should the NDA and Service Agreement Actually Cover?
An NDA addresses confidentiality. The working agreement must also say what the provider is allowed to do with the data. Identify the approved workflows and systems, the agency's ownership of records, permitted storage and transfer, whether subcontractors can participate, and how the provider handles records when the engagement ends. Define how suspected incidents are reported, who cooperates with investigation, and how the agency obtains the information it needs to assess its own notification duties.
Do not treat a promise of “compliance” as a substitute for those terms. A provider cannot decide every state, carrier, and client obligation on the agency's behalf. Nor should a confidentiality clause obscure whether the provider's working tools copy files, where those copies reside, or whether an assistant may use an unapproved AI or transcription tool with policyholder information. Put approved tools and exceptions in writing. The agency's legal reviewer can decide which contract language fits the actual assignment.
The distinction matters in a routine handoff. Suppose the assistant receives an application by email, saves it to a personal drive to work after hours, and later updates the AMS. The AMS activity may look complete, but the agency has lost control of the extra copy. A specific rule about approved storage, deletion, and supervision would make the behavior reviewable before it becomes routine.
How Should an Agency Grant AMS and Carrier Portal Access?
Grant access to named people through approved accounts, with the lowest practical permission for each role. Record who requested access, who approved it, what the user can do, which systems are included, and when it will be reviewed or removed. Avoid a shared producer login simply because it is quicker to start. If a carrier portal cannot support the proposed role or multifactor authentication, resolve that constraint with the carrier and the agency's system owner before assigning the task.
NIST's small-business MFA guidance explains the extra protection MFA provides when a password is compromised and recommends enabling it on accounts that offer it. For outsourcing, the test is operational: can the named assistant sign in with an approved method, can the agency see the activity, and can access be removed promptly without disrupting the producer's own account?
Try one controlled transaction before granting a full book. For example, give an assistant a sanitized certificate request and ask them to show the request source, the information they used, the draft they prepared, and the AMS activity they would leave for review. The agency then checks the proposed permissions and the handoff for coverage or wording questions. A successful demo of typing speed does not establish the access boundary; the complete record does.
Where Do Policy Documents and Work Notes Belong?
The agency should choose approved channels for intake, work, review, and final filing. Client email, carrier downloads, ACORD forms, loss runs, and issued documents may arrive through different systems. The assistant needs an instruction for which version is authoritative, where to store it, and how to handle a mismatch. A note that says “processed” without the source, action, exception, and reviewer leaves the agency with a weak audit trail.
Agree on local-download, printing, forwarding, and retention rules. Decide whether screenshots and exports are permitted, whether personal email or consumer file-sharing tools are prohibited, and how data in any approved work platform is deleted. If a new tool is proposed later, assess it before entering live client material. These controls should appear in a real process for policy servicing handoffs, where a missing endorsement or an incorrect document version can carry into the next transaction.
Documentation quality is also a compliance issue. The support person can prepare a draft, index evidence, and flag missing facts. The agency retains its review and approval responsibilities for substantive coverage, client advice, and binding decisions. A permissions matrix and a clear handoff should reflect that division, rather than relying on a general statement that the assistant is “insurance trained.”
What Should Happen If an Incident or Exception Occurs?
Define two paths. An operational exception might be a mismatch between the client's instructions and the carrier's issued document. A security event might be a misdirected file, lost device, suspicious login, or unapproved disclosure. Both need an owner and a record; the security path also needs a rapid contact channel, containment steps, evidence preservation, and enough initial facts for the agency to assess its duties.
Write an incident notice rule that gives the provider a named agency contact and a trigger for promptly reporting suspected events, even when the full scope is not known. Require an update as facts develop. Ask who will preserve logs, identify affected systems and data, disable access, and support the agency's investigation. Avoid copying a single notification deadline from the NAIC model into every contract: the governing requirements and trigger may differ by state, incident, and agreement. Set the vendor's notice timing early enough for the agency to meet the requirements that actually apply.
Review a redacted incident exercise or response flow, not just the existence of a plan. The NAIC model law's incident provisions illustrate the importance of investigating an event involving a third-party system and documenting the outcome. The agency should test its own reporting path alongside the provider's process.
How Do You Monitor the Arrangement After Go-Live?
Security review continues after procurement. Reconcile the named access list with the people actually assigned. Sample a few completed transactions for source documents, AMS activity, exceptions, and reviewer approval. Check whether an absence replacement had the right access and whether old permissions were removed. Revisit the assessment when the provider changes staff, location, tools, subcontractors, or scope.
An operations manager can keep a compact register: task, system, named user, approval owner, granted role, last review, open exception, next review. This is more useful than a binder of policies that no one connects to the daily work. At exit, close the task queue, export or return agency records in the agreed format, revoke AMS and portal access, and request the agreed deletion or retention confirmation. The agency should preserve the records it is required to retain.
How Does United Alliances Fit This Review?
United Alliances offers insurance back-office outsourcing for administrative work such as application entry, policy processing, document indexing, and carrier follow-up. Its published Security & Compliance page describes role-based access, unique credentials, MFA where supported, remote-work controls, logging, incident procedures, and confidentiality training. Its data ownership statement describes client control and return or deletion of client records. These are published descriptions to verify against the proposed workflow; they are not a substitute for a signed scope and operational evidence.
The company describes its program as ISO/IEC 27001-aligned. That language should not be read as a claim of certification. If ISO assurance is a purchase requirement, ask for the specific evidence and scope your agency requires. The security questionnaire should be applied to United Alliances just as it would be to another candidate; its page says relevant documentation and questionnaire responses may be shared during due diligence. For the broader decision about workflow fit and supervision, see its insurance back-office partner selection guide.
Make the First Access Decision Deliberate
Pick one real workflow, redact a sample packet, and ask a candidate to show the people, systems, permissions, data path, review point, and exit path. Write down any unresolved issue and its owner before live access. That small exercise tests whether the provider's security statements reach the policy record your team actually handles.
If you are considering an assigned insurance support team, discuss the task scope and security review with United Alliances. Bring your AMS roles, carrier portal constraints, and a sample handoff so the discussion can be specific.